Targeted support
Steering stays with you
A NIS-2 scope analysis, a DORA gap analysis, an audit or a security assessment: a defined brief with a documented result.
We do not only advise on IT and information security, we implement: assess the security level, design the target architecture and processes, put measures in place and keep operations secure on an ongoing basis.
Assessed, not assumed
Scope and security level are established and documented
Ready for audit
Policies, controls and incidents are findable and evaluable on audit day
Legal included
Contracts, notification duties and liability handled by the lawyers in our firm
Lived day to day
We check whether measures work, rather than describing them once
What we take on
IT security is not a product, it is a process. We own it together with your internal owners.
Typical triggers: Usually one event tips the balance: an audit, a customer requirement, a security incident, or a new directive with a fixed deadline.
NIS-2 or customer requirements call for evidence that stands up
Security measures are documented but not lived day to day
IT owners are tied up in day-to-day operations
There is no independent review of the actual security level
Services in detail
From the inventory through to ongoing operations. Commissioned individually, built on one another.
Security does not come from individual tools, but from a managed information security system. We capture protection needs, build the ISMS to ISO 27001 and, if you wish, provide the information security officer who runs it on an ongoing basis.
What we handle
Inventory and determination of protection needs
External information security officer for set-up and ongoing operations
Build an ISMS to ISO 27001 and support through to certification
Audit against BSI IT-Grundschutz, from a basic check to a full audit
Security policies, risk and measures management
IT security, backup and erasure concepts
Examples from our work
The first question is not which measures are needed, but whether the directive applies at all. We establish whether you are in scope in a documented way, then build risk management, the notification chain and supplier duties so they stand up to an audit.
What we handle
Scope analysis for your company
An audit plan per department and delivery of the audit
Build-out of risk management
Set-up of the contact point and notification chain
Adjustment of contracts and evaluation of partners
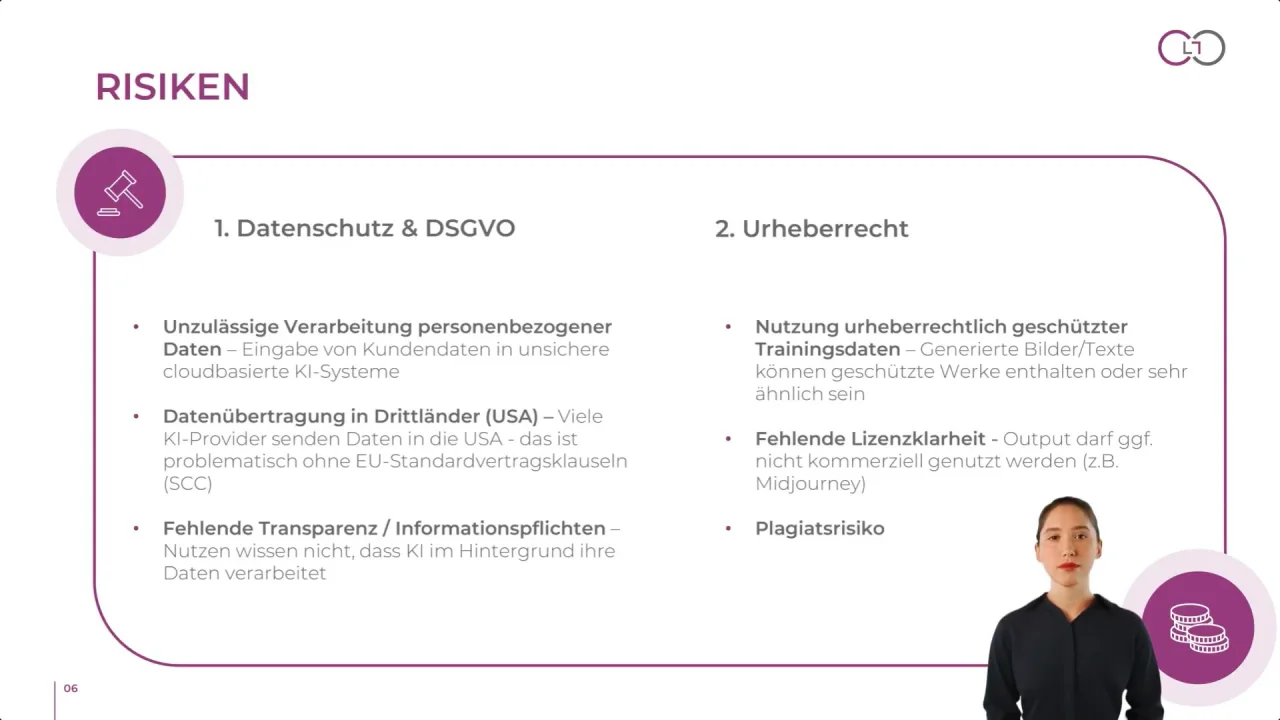
Training portal
The directive places personal duties on the management layer and also requires training for employees. We roll out the modules through the portal and document who completed them and when, so the evidence is there on audit day.
Modules on IT security, BSI IT-Grundschutz, NIS-2 and using AI safely
A dedicated module for management and the leadership layer, who themselves are under a duty
Assignment by role, legal entity and site, instead of one mandatory date for everyone
Attendance status and certificates as control evidence for audits and customer assessments
For financial companies and their ICT service providers, regulation meets contract law. In a gap assessment we show where you stand, build ICT risk management and draft the outsourcing contracts together with the lawyers in our firm.
What we handle
Gap analysis against DORA and sector-specific requirements
Build-out of ICT risk management
Review and sharpen IT and emergency concepts
Draft third-party and outsourcing contracts in a legally sound way
Training and workshops for specialist and leadership teams
There is often a gap between documented and actual security. We check technically, run controls with deadlines and owners, and record measures so that audits and customer assessments do not depend on searching a file store.
What we handle
Vulnerability analyses, technical security checks and penetration tests
Audit-proof documentation of all measures and controls
Control monitoring with deadlines and owners
Support for audits and customer assessments
Incident handling including notification paths
Ongoing updates as the threat landscape and regulation change
Ways of working together
You decide how much information-security responsibility goes outside. The three models sit side by side and often run in parallel. IT support and day-to-day system operations stay with you. You can start at any scale, and move between models at any time.
Steering stays with you
A NIS-2 scope analysis, a DORA gap analysis, an audit or a security assessment: a defined brief with a documented result.
Process ownership sits with us
We build the ISMS, support you through to certification and keep it running: monitor controls, handle incidents, support audits and customer assessments.
Information security and team sit with us
We also take on your people: information security as a whole – policies, ISMS, the appointed information security officer and the evidence, including your security owners. We do not take on the helpdesk, endpoints or system operations.
How we work
First the actual security level, then the target picture, then implementation, then the controls that carry the evidence on audit day.
We capture protection needs, risks, existing measures and evidence, and expose gaps between documentation and practice.
We draft the target picture, policies, roles and controls, aligned to regulation, customer requirements and effort.
We put measures in place, introduce the ISMS, involve service providers and document in an audit-proof way in CLAIR.
We monitor controls, support audits and adjust measures as threats and requirements change.
Technology in the background
Policies, controls, incidents and measures are kept in CLAIR, with deadlines, owners and a status overview. Audit extracts are produced at the press of a button.
Modules in use: Compliance Management · Incident management · Service-provider steering · Reporting & Cockpits
More about CLAIR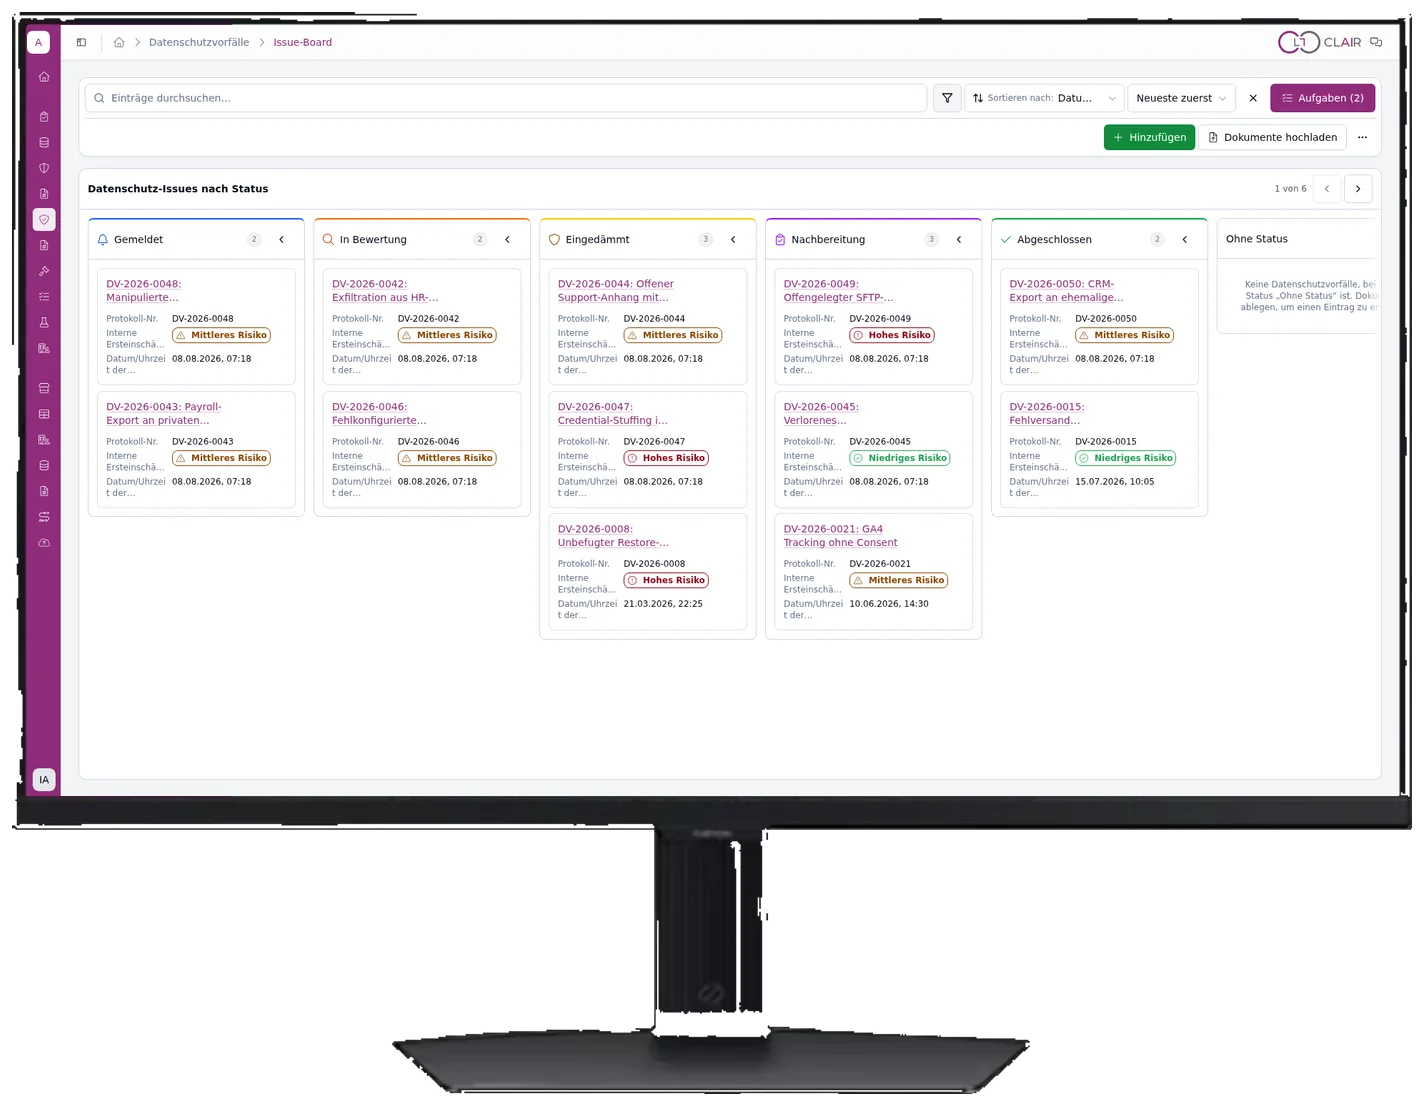
Examples from our work
All case studies on IT securityThree examples from live mandates: from the scope analysis through set-up to ongoing operations.
Technology
A grid operator brings information on plots of land, contracts and rights of use together in a central digital solution.
Read case study
Technology
An integrated digital process connects existing systems, reduces manual coordination and speeds up the handling of claims.
Read case study
IT security
An international technology provider steers NIS2-relevant security incidents, reporting deadlines and authority communication even when internal systems fail.
Read case studyFrequently asked questions
We can take on information security in full, including the team if you wish. We do not take on IT support, the helpdesk or day-to-day system operations.
We clarify that in the scope analysis based on sector, size and supply relationships. The result is a documented classification, not an assumption.
Contracts, notification duties and liability questions are handled by lawyers in the same group, without a second provider.
An inventory usually takes a few weeks. Building a management system you can stand behind is a programme over several months.
We review your IT and information security processes and show which measures actually have an effect.
Get in touch without obligationRather get in touch directly
Tell us briefly what you need. We pass your enquiry on to the colleagues who work on your topic.
Form loading …